OHS compliance
Ensure Educational Excellence and OHS Compliance with Sancert
The General Data Protection Regulation (GDPR) is the world’s leading data protection law. It governs how organisations collect, use, store, and transfer the personal data of individuals in the European Union (EU). Non-compliance can result in fines of up to €20 million or 4% of global annual turnover, whichever is higher.
A GDPR compliance review is relevant if you:
Need to verify your compliance programme before a procurement process, investor review, or regulatory enquiry.
Want independent assurance that your data protection practices meet regulatory requirements.
Have built out GDPR controls internally and need external validation.
Operate across multiple jurisdictions and need clarity on your obligations.
GDPR: Are you Covered?
Knowing that GDPR applies to your organisation is one thing. Being able to demonstrate that your compliance programme is working is another.
Take our free GDPR Compliance Check to identify potential gaps across the key areas of GDPR governance, data protection and security.
A quick self-assessment to understand where your organisation stands and where potential gaps may exist.
This self-assessment is intended as a general indication of your organisation's GDPR readiness. It is not legal advice or a formal determination of compliance.
A self-assessment can highlight potential gaps. A Sancert GDPR Review provides an independent assessment of your current position, identifies areas requiring attention and gives you a practical roadmap for improvement.
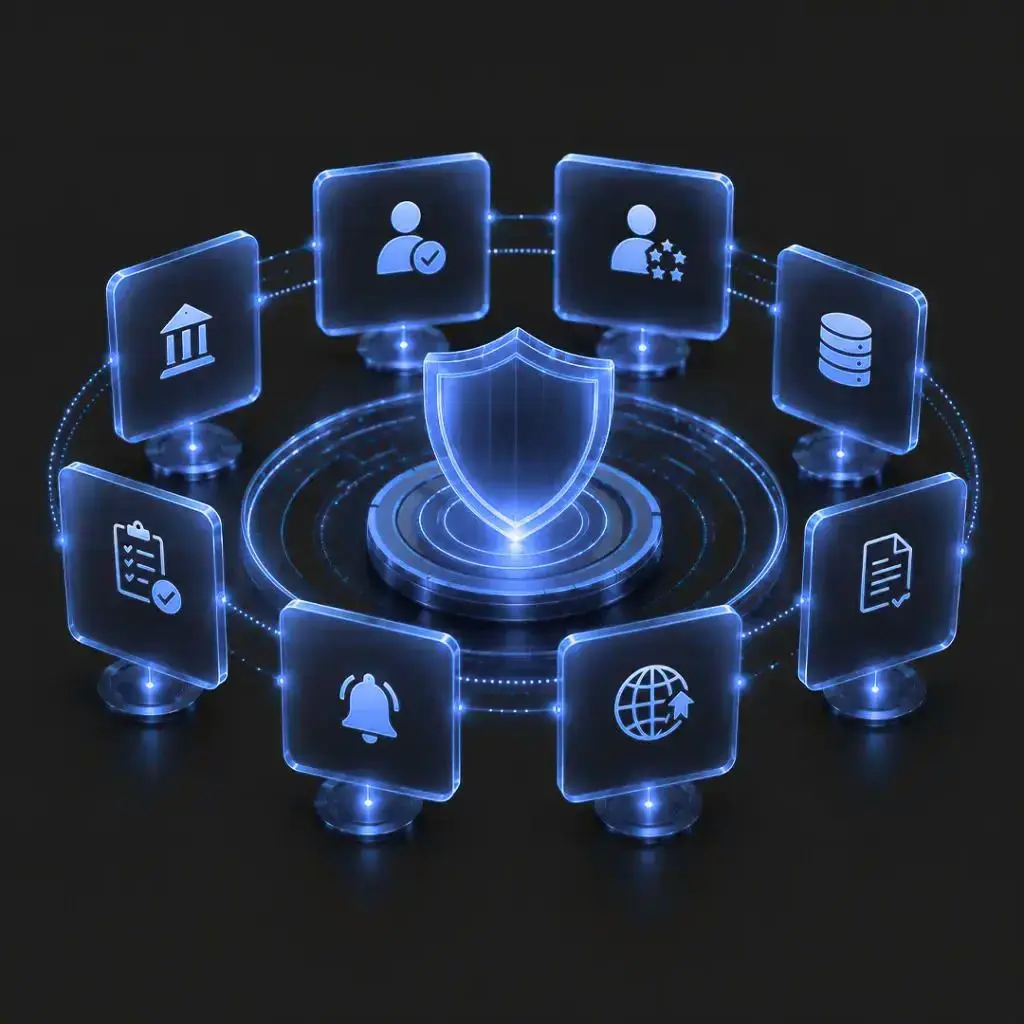
Find out about the GDPR reviewOur structured compliance review assesses your compliance posture across all key GDPR obligation areas, including:
An independent GDPR compliance review delivers more than a compliance tick-box:
Documented, independently verified compliance reduces your exposure to fines and enforcement action.
Enterprise procurement, investor due diligence, and client onboarding processes increasingly demand evidence of data protection compliance. A compliance review report gives you that evidence.
The review process surfaces exactly how your organisation handles personal data, creating a cleaner, better-governed picture of your information flows.
Knowing where your gaps are means you can address breach detection and notification weaknesses before they become a regulatory problem.
Our assessments carry the weight of over 20 years of compliance experience.
Where GDPR intersects with POPIA, ISO 27001, or other regulatory obligations, our team understands the overlaps, reducing duplication and maximising the value of your review.
No open-ended engagements, no surprises.